
Offensive
Penetration testing
Scoped tests of web apps, networks, and exposed services. We show what an attacker can do, then sit with you on the fix list.
Penetration testing, audits, and B2B retainers for SMEs and institutions — for shops that cannot hire a full-time security team.
This page is company services only. Students and individuals who want to learn use the eight training tracks — not this quote flow.
Scoped tests of web apps, networks, and exposed services. We show what an attacker can do, then sit with you on the fix list.
Short, practical sessions for staff: phishing, passwords, devices, and what to do when something feels wrong. Built for small teams, not Fortune 100 slideware.
Baselines for servers, identity, endpoints, and cloud. Close the defaults that stay open because nobody had time.
Preserve evidence, reconstruct what happened, and give leadership a clear picture — without pretending every shop has a SOC.
Segmentation, remote access, wifi, and the boring architecture decisions that stop a laptop compromise from becoming a company-wide event.
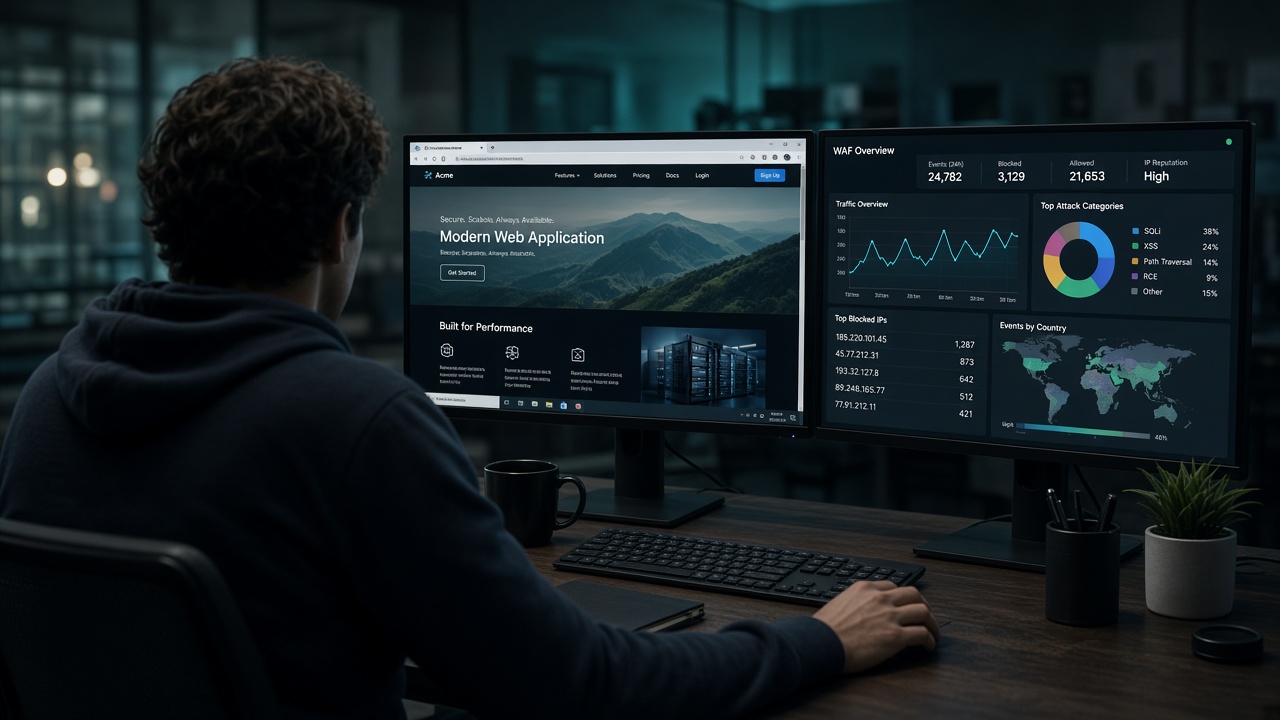
Review the app your customers use. Deploy and tune a web application firewall so it blocks abuse without blocking checkout.
You are online, you take payments or hold client data, and you do not have a security department. We work in scopes you can budget — assessments, hardening sprints, awareness days, WAF setup.
Protect program and donor systems. Training for your people is a separate learner track if you want it.
Tell us the environment. We reply with work, not a syllabus.